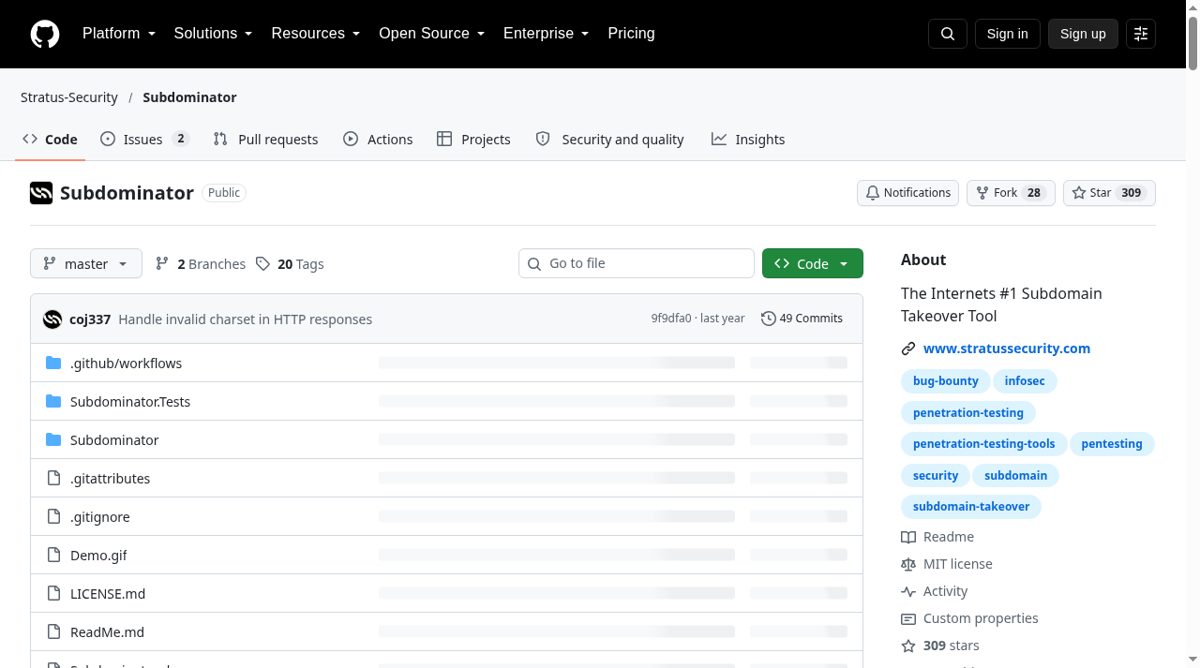
Subdominator is an open source tool for finding subdomain takeovers, the dangling DNS records that let an attacker claim a company's forgotten subdomain. It was built by Stratus Security, a penetration testing consultancy, after the team decided the existing open source options were not good enough for their engagements. The tool was used internally for some time before being released publicly, and it carries an MIT license with several hundred stars on GitHub.
The scanner checks subdomains against a database of takeover fingerprints, maintained as a custom fingerprints file in the repository in the tradition of the can-i-take-over-xyz project. Ready built releases are published for Windows and Linux, so there is no build step for most users, and the project includes a test suite and CI. Because it started life as an internal pentesting tool, its design prioritizes the checks practitioners actually run during assessments.
Subdominator is a specialist instrument: it does one class of reconnaissance rather than full vulnerability scanning, and it belongs in the toolkit of security teams, bug bounty hunters and admins auditing their own DNS. Stratus Security maintains it alongside its commercial penetration testing services, and the company's blog tells the development story for anyone evaluating its approach. As with any scanner, only point it at infrastructure you are authorized to test.