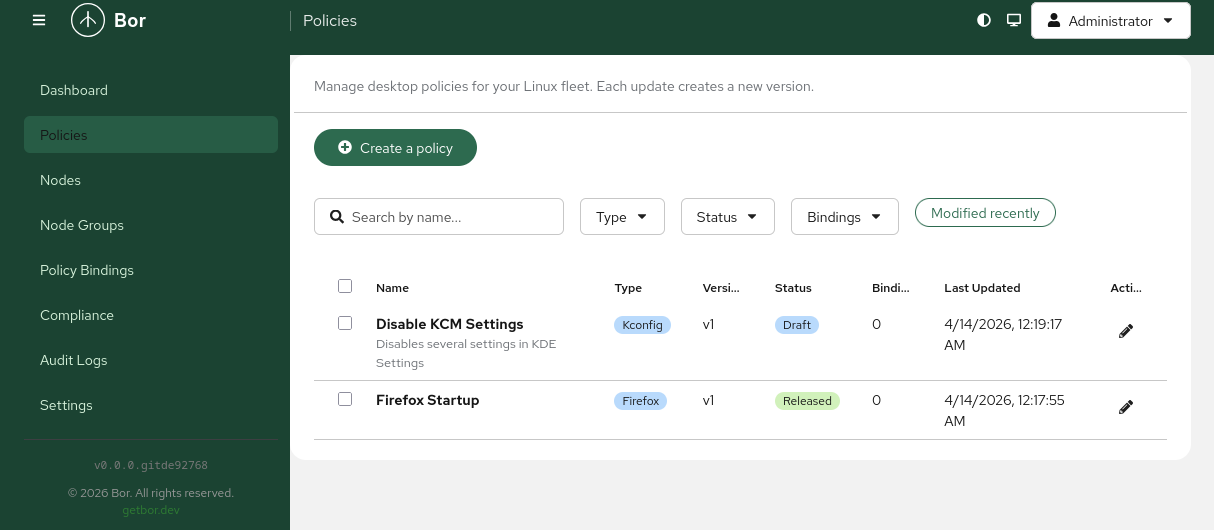
Bor
Open-source policy management for Linux desktops
About Bor
Bor — Open-source policy management for Linux desktops. It was shared on Show HN in 2026 and received 197 upvotes on Hacker News. Bor v0.8.0 is out. This release adds three new policy types — Thunderbird, Microsoft Edge for Business, and Firewalld zones — alongside a full web UI overhaul, finer-grained RBAC, and a dedicated security hardening pass. The complete changelog is on the GitHub release page.
Thunderbird policy type Mozilla Thunderbird can now be managed on enrolled desktops with the same mechanism used for Firefox ESR. The agent writes the managed policies.json that Thunderbird expects, merged from all bound policies, and removing the last policy restores the original file. The web UI provides a tree-based editor with the Edge policy catalogue, JSON validation, and a setting preview before enabling. Like all other managed files, the zone files are tamper-protected. Polkit: variable conditions Polkit rules now support variable conditions via action.lookup() , so a rule can match on action variables — for example allowing mounts only for removable drives. Also fixed: multiple action IDs in one rule are now correctly joined with || . Per-action RBAC User and role administration is now guarded by per-action permissions instead of a single blanket permission, allowing finer-grained delegation of admin duties. The highlights: URL routing — every page has a real URL with working browser back/forward and deep links; expired sessions redirect to login; a global error boundary prevents white-screen crashes. Full-page policy editor — the policy editor is now a routed page ( /policies/:id/edit ) instead of nested modals. Security hardening This release includes a dedicated hardening pass: Agent identity is now strictly bound to the mTLS client certificate, and MFA/RBAC enforcement paths were hardened on the server. Legacy SHA-256-encrypted TOTP secrets are transparently migrated to HKDF-derived encryption on first read. The Ubuntu PPA and Fedora COPR repository import helpers now block redirect-based SSRF; only allowlisted redirect targets are followed. Audit log CSV export is guarded against spreadsheet formula injection. The auto-generated initial admin password is no longer printed to the server log (where it would land in journald or centralized logging); it is written to a root-only file instead. The server TLS certificate is automatically regenerated when its SANs no longer match the configured hostnames. All open Dependabot alerts were resolved, including the react-router RSC CSRF advisory (GHSA-qwww-vcr4-c8h2). Server and agent dependencies were bumped, including gRPC 1.82.1 and golang.org/x/crypto 0.52.0. Download Packages for Debian/Ubuntu, RHEL/Fedora/SUSE, Alpine Linux, and Arch Linux across x86_64, aarch64, and ppc64le are available on the Download page.
Community AMA
Ask the founder anything!
No questions yet. Be the first to ask!
Community Perks
Check back soon for exclusive offers
We're cooking up something special with 'Bor' to bring you exclusive perks!
The kitchen is busy - amazing deals are coming soon! 🔥
You Might Also Like...
OpenFreeMapOpen-Source Map Hosting
MemoriesFOSS Google Photos alternative built for high performance

PaisaOpen-Source Personal Finance Manager
FrameOSoperating system for single function smart frames
Alternatives to Bor: OpenFreeMap, Memories, Paisa, FrameOS · Compare all alternatives ›